Locked In and Paying for It: The Architectural and Contractual Mechanics of Enterprise Vendor Dependency
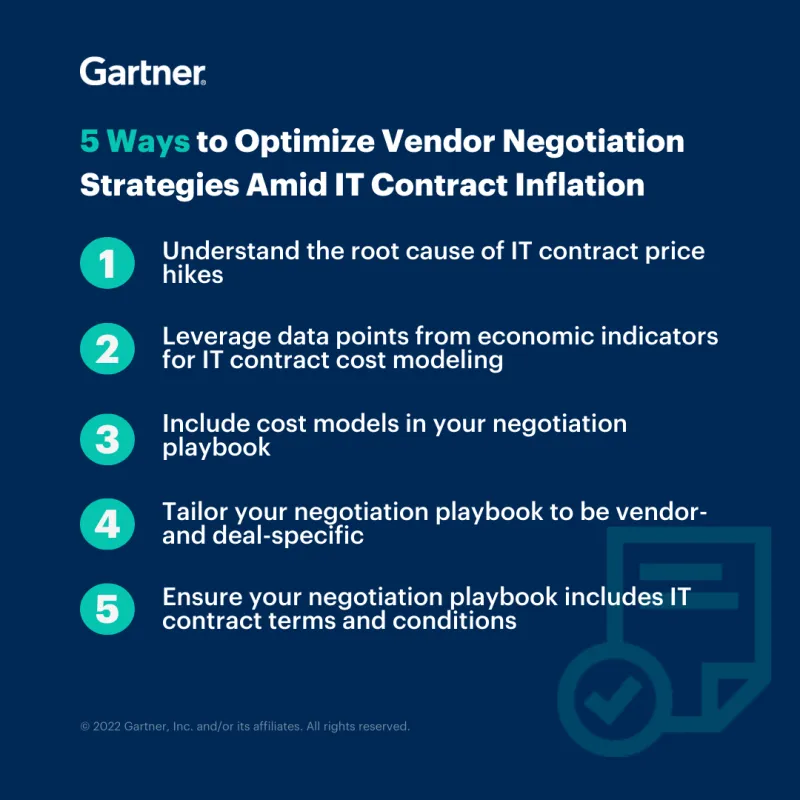
Photo: enterprise contract negotiation legal documents technology vendor meeting, via emt.gartnerweb.com
The pitch is familiar. A major technology vendor presents an enterprise client with a compelling platform: deeply integrated, richly featured, backed by an impressive support organization, and priced attractively — at least for the initial contract term. Three years later, renewal negotiations look entirely different. The client's entire operational infrastructure is entangled with the vendor's proprietary APIs. Data extraction is technically possible but practically prohibitive. The cost of switching has grown to the point where the vendor's renewal pricing is, in effect, a ransom.
This is not a story about a vendor behaving unethically. In most cases, the mechanisms that produce this outcome are disclosed, if not prominently, in the original contract. The problem is that enterprise procurement and legal teams are evaluating these agreements under time pressure, with an emphasis on closing the deal rather than modeling the exit. By the time the dependency becomes visible, unwinding it is genuinely expensive.
Understanding how vendor lock-in is constructed — architecturally and contractually — is the first step toward avoiding it.
The Architecture of Dependency
Proprietary APIs are the most common architectural mechanism for creating switching costs. When a vendor's platform exposes functionality exclusively through interfaces that have no open equivalent — and when an enterprise's internal systems are built to consume those interfaces — the cost of migrating to an alternative platform includes rewriting every integration that touches the vendor's API surface.
This is not inherently problematic if the API design is stable, well-documented, and the vendor relationship is sound. The risk emerges when the vendor controls both the API specification and the pricing of access to it. Changes to API terms, rate limits, or authentication requirements can impose significant operational costs on clients with no practical recourse other than absorbing the change or undertaking a migration they were not prepared for.
Data portability restrictions represent a second architectural lever. Enterprise platforms accumulate years of transactional history, configuration data, and operational records. The technical formats in which this data is stored — and the mechanisms by which it can be exported — are often defined by the vendor. Export tools may exist but produce outputs that require substantial transformation before they are usable in an alternative system. In some cases, complete data extraction requires vendor cooperation that is not guaranteed under the base contract terms.
A third mechanism is ecosystem entanglement. Vendors that operate broad platform ecosystems — covering infrastructure, identity, analytics, and application development — benefit when enterprise clients adopt multiple services within the same ecosystem. Each additional service deepens the integration surface and increases the operational complexity of a hypothetical migration. The individual services may each be competitively priced; the aggregate switching cost of the entire ecosystem is what ultimately constrains the client's negotiating position.
The Contractual Infrastructure of Lock-In
Architectural dependency is reinforced by contractual structures that are worth examining with considerable care before signing.
Volume commitment tiers are a standard feature of enterprise software agreements. Clients receive meaningful per-unit discounts in exchange for committing to minimum consumption levels over a multi-year term. These arrangements are financially rational for clients with predictable demand. They become problematic when demand shifts — through organizational restructuring, a strategic pivot, or a competitive disruption — and the client is obligated to pay for capacity it no longer needs while simultaneously being unable to reallocate budget toward alternatives.
Licensing portability restrictions limit the conditions under which software licenses can be transferred, reassigned, or deployed across different infrastructure environments. Clients that acquire licenses under terms optimized for on-premises deployment may find that migrating to a cloud environment — or vice versa — triggers renegotiation at current market rates rather than honoring the economics of the original agreement.
Data egress clauses, or the absence of them, deserve particular scrutiny. Contracts that do not explicitly guarantee the client's right to extract their own data in a machine-readable, vendor-neutral format create a dependency that grows more consequential with every year of platform usage. The absence of a data portability guarantee is not a neutral omission. It is a structural advantage for the vendor in any future commercial negotiation.
Finally, audit rights provisions — which permit vendors to audit client deployments for licensing compliance — can be deployed strategically during contract renewal discussions. An audit finding, even a minor one, shifts negotiating leverage to the vendor at precisely the moment when the client is attempting to renegotiate terms.
Designing for Portability Without Sacrificing Integration
The response to vendor lock-in risk is not to avoid commercial platforms or to build everything internally. That approach trades one set of costs for another. The appropriate response is to design enterprise systems in ways that preserve optionality without sacrificing the integration depth that makes commercial platforms valuable.
Abstraction layers between internal systems and vendor APIs are a foundational architectural practice for maintaining portability. When internal applications communicate with a vendor platform through an internal service layer that translates between the vendor's interface and a vendor-neutral internal contract, migrating to an alternative platform requires updating the translation layer rather than modifying every consuming application. This pattern imposes a modest upfront engineering investment that pays for itself substantially in any future migration scenario.
Data sovereignty practices — including regular, automated exports of all platform data to client-controlled storage in open formats — ensure that the client's operational history is never exclusively held by the vendor. This is not primarily a security measure, though it serves that function as well. It is a negotiating asset. An enterprise that can demonstrate it holds a complete, current, portable copy of its own data negotiates from a materially stronger position than one that does not.
Multi-vendor architecture, where operationally feasible, distributes dependency across multiple providers and prevents any single vendor from achieving the leverage that comes with monopoly status in a client's technology stack. This approach requires more integration work and more vendor management overhead, but for critical infrastructure categories, the cost is generally justified.
What to Negotiate Before You Sign
The most cost-effective point to address lock-in risk is before the contract is executed. Several provisions are worth pursuing in every enterprise technology agreement.
Explicit data portability guarantees should specify the format, completeness, and timeline for data export upon contract termination. These provisions should be in the main agreement body, not in a separately negotiated schedule that can be modified without triggering a full contract review.
API stability commitments — including advance notice periods before breaking changes are introduced — protect the client's integration investments and provide a contractual basis for cost recovery if the vendor fails to honor them.
Termination assistance obligations, requiring the vendor to provide reasonable technical cooperation during a transition period after contract end, are standard in well-negotiated enterprise agreements and should be treated as a non-negotiable baseline.
Price protection provisions that cap renewal rate increases, at least for a defined period, limit the vendor's ability to exploit the switching costs that accumulate over the contract term.
None of these provisions are unusual asks. Vendors that resist them are, in effect, signaling that their commercial model depends on the client's inability to leave. That signal is worth taking seriously before the contract is signed.